Access management
Review organization members, teams, and the permissions available for your WhoDB deployment.
Review the implementation
Security / Control and visibility
Review access management, credential handling, and deployment controls against the requirements of your own environment.
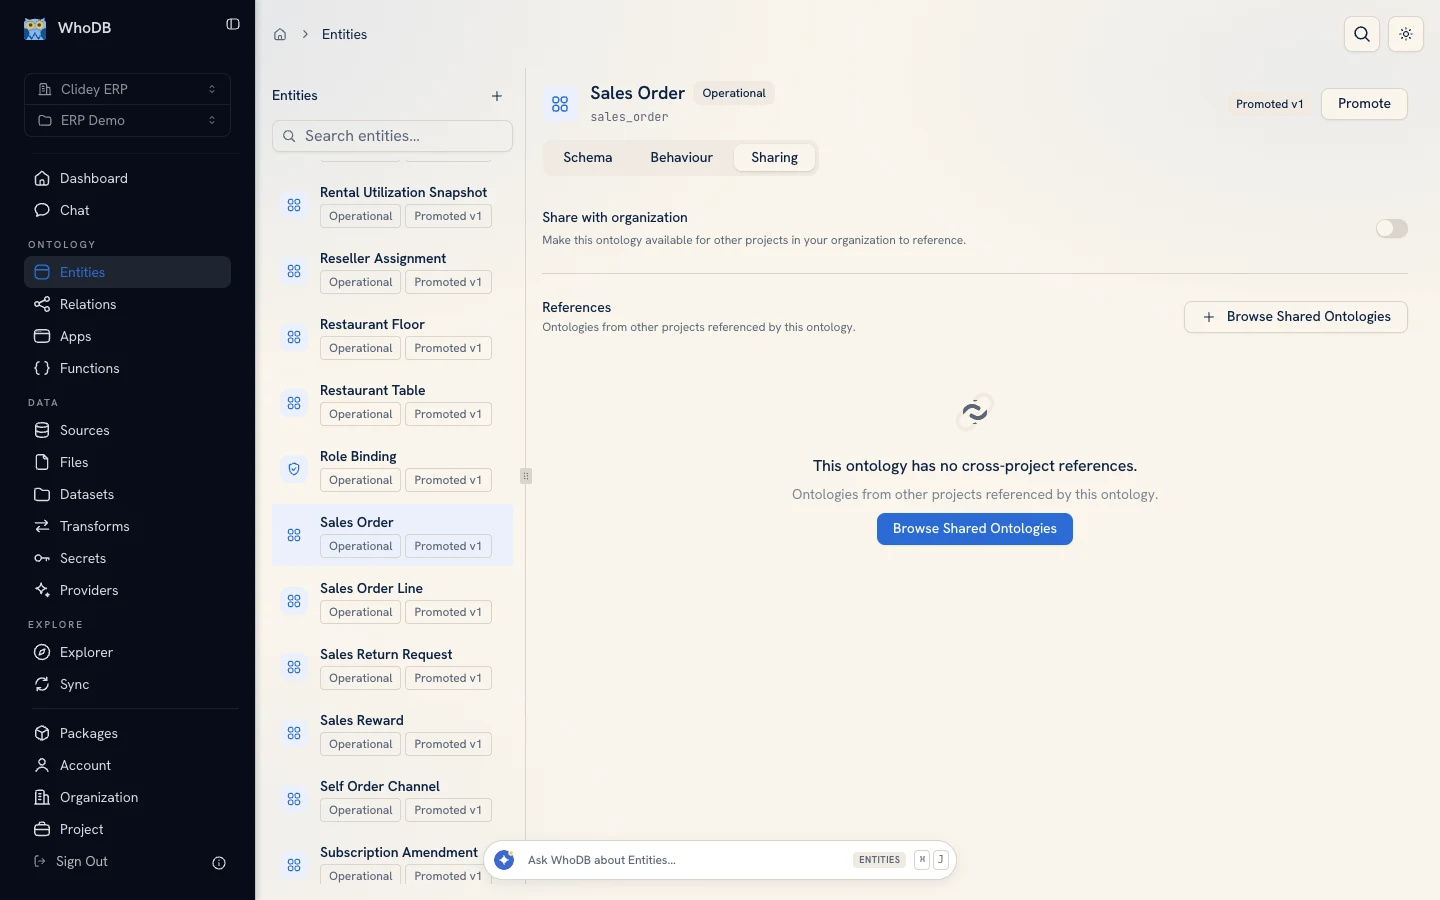
Review organization members, teams, and the permissions available for your WhoDB deployment.
Review the implementation
The self-hosted installation guide documents encrypted credential storage and secure session cookies. Review Cloud or Managed Private handling with our team.
Review the implementation
For self-hosted teams, the setup guide covers HTTPS, reverse proxies, and network restrictions. Managed deployment controls depend on your architecture.
Review the implementation
Review available workflow history alongside application, proxy, and database-native logs for your environment.
Review the implementation
Evaluate the controls and documentation that apply to your edition and deployment. Ask for current evidence and agreements before making compliance decisions.
Public documentation
Installation and team setup guides describe credential storage, HTTPS configuration, session settings, and database-side access controls.
Review with our team
Map identity, network, data location, and logging requirements to the deployment model you are evaluating.
Confirm current scope
Request the current status of audit reports, privacy terms, and any regulated-workload agreements before relying on them for procurement.
Walk through identity, network, data location, retention, and compliance requirements with our team for the deployment you are considering.
We take security disclosures seriously. If you discover a potential vulnerability in WhoDB, please submit a report through GitHub private vulnerability reporting.
Open a private report →